The Split-Tunnel Trap: Why Home Wi-Fi Spells Danger for Corporate VPNs
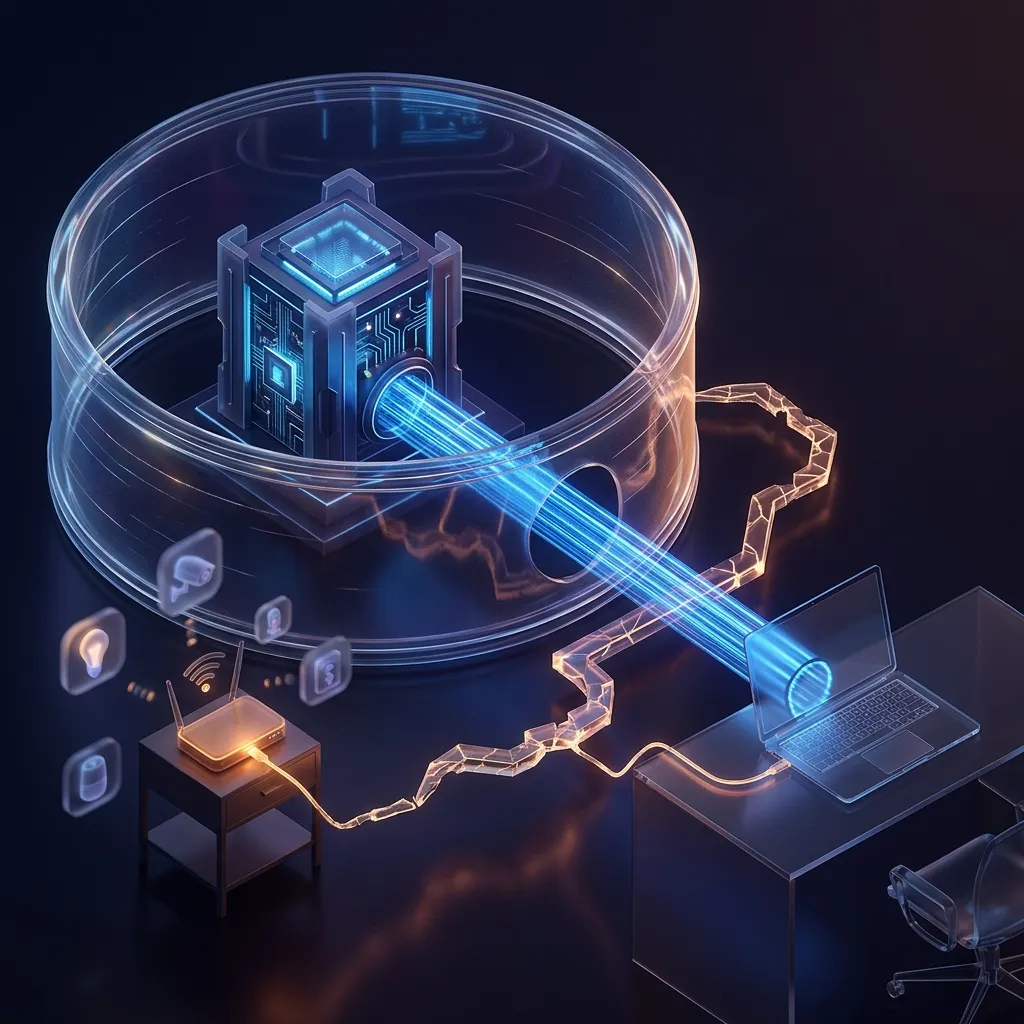
When companies moved their staff to remote work, IT helpdesks faced an immediate wave of tickets. Remote employees complained that connecting to the corporate VPN broke their home office setup. They could no longer print shipping labels on their wireless printer, airplay Spotify to their smart speaker, or access local network storage.
To keep everyone happy and reduce ticket volume, system administrators turned on a popular setting in the VPN client: Allow local LAN access, commonly known as split tunneling.
The complaints stopped. Printers worked again. But with a single checkbox, the company compromised the security boundary of its corporate network.
The Armored Car with an Open Trunk
A corporate VPN exists to create an encrypted tunnel between an employee’s laptop and company servers. It shields sensitive traffic from snooping on untrusted networks, whether that is a hotel lobby or a coffee shop.
Enabling local LAN split tunneling is like building an armored transport truck with bulletproof glass and reinforced doors, but leaving the back tailgate unlatched so the driver can grab groceries from the trunk.
If an attacker cannot pierce the armor from the outside road, they simply crawl in through the unlatched tailgate while the truck is parked in a residential driveway.
In a home environment, an employee’s work laptop does not sit in isolation. It shares a local subnet with budget smart bulbs, unpatched Android TV boxes, gaming consoles, and personal laptops used by family members to browse unvetted websites. Most consumer routers run years-old firmware with known vulnerabilities.
When split tunneling is active, the work laptop acts as a dual-homed bridge. It has one interface inside the secure corporate intranet and another interface directly exposed to the unsegmented home subnet.
How Local Threats Pivot Across the Tunnel
Attackers rarely target the corporate VPN server directly when softer paths exist. A common intrusion chain unfolds quietly on the home network:
- The Initial Compromise: A cheap IoT device or personal tablet on the home Wi-Fi is infected via a known vulnerability or malicious download.
- Subnet Reconnaissance: The malware scans the local IP range (typically
192.168.1.0/24) looking for active devices. It finds the company laptop. - Lateral Movement: Because local network traffic bypasses the VPN tunnel, the infected device can probe the laptop’s open ports, exploit unpatched local services, or perform ARP spoofing to intercept traffic before it ever reaches the VPN encryption layer.
- Intranet Traversal: Once malicious code gains a foothold on the work machine, it routes outbound packets through the active corporate VPN tunnel directly into internal databases, code repositories, and staging environments.
To the corporate intrusion detection system, the suspicious traffic appears to originate from an authenticated employee with valid credentials.
Designing a Safe Remote Boundary
Forcing 100% of all traffic through a full tunnel can strain server bandwidth and still frustrates staff who genuinely need home printing. Fixing the vulnerability requires granular policy enforcement:
- Host-Based Firewall Isolation: Configure endpoint management profiles (MDM) to block inbound connections from local subnet addresses, even when local outbound printing is allowed. A laptop can initiate a print job to a specific IP without accepting arbitrary incoming packets from other home gadgets.
- Network Access Control (Zero Trust Network Access): Move away from broad subnet routing. Instead of giving an employee full access to the entire
10.0.0.0/8corporate network upon connection, grant access on a per-application basis using verified identity and device health checks. - Dedicated VLANs for Remote Workstations: For executive or high-privilege staff, provide pre-configured travel routers or advise setting up an isolated Guest Wi-Fi network at home. Keeping work hardware off the primary home subnet eliminates exposure to smart appliances and family devices entirely.
A secure VPN tunnel is only as dependable as the endpoints on either side of it. Book a consultation with us to audit your remote workforce configuration and build network policies that protect your core systems without breaking everyday productivity.